PyTorch 2.15 Rollback Has Two Boundaries. Only One Is a Setting.
PyTorch 2.15 has an NCCL fallback you can set for one release and a checkpoint boundary you cannot. Plan the upgrade around the second.
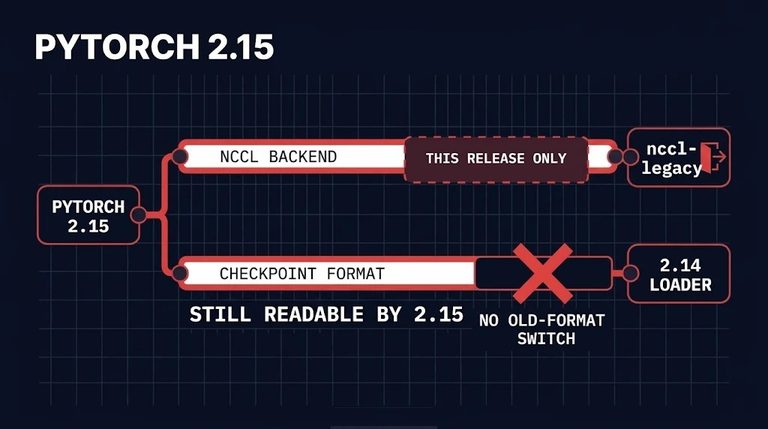
PyTorch 2.15 has an NCCL fallback you can set for one release and a checkpoint boundary you cannot. Plan the upgrade around the second.
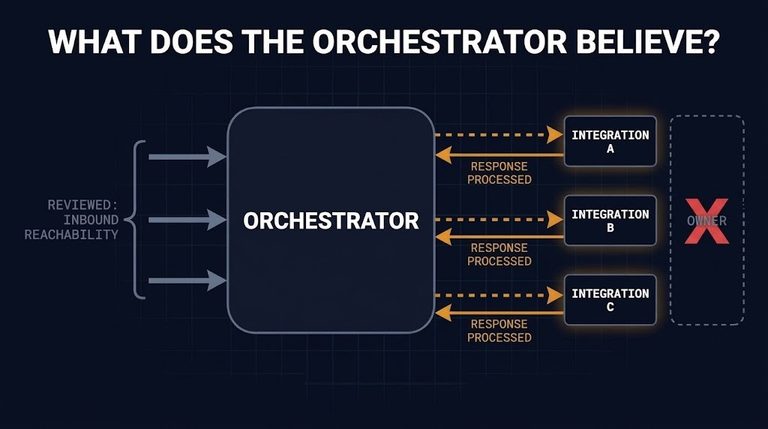
Integration endpoint trust governs what an orchestrator processes from the destinations it calls. What Arista’s VeloCloud Orchestrator advisory establishes, what it does not, and who owns the boundary.
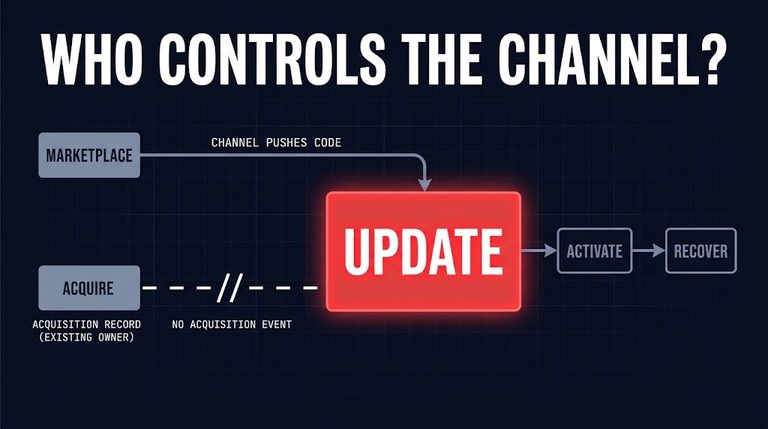
Extension update authority decides what runs on engineering endpoints. What the October 29 Cursor incident establishes, what it does not, and what recovery requires.
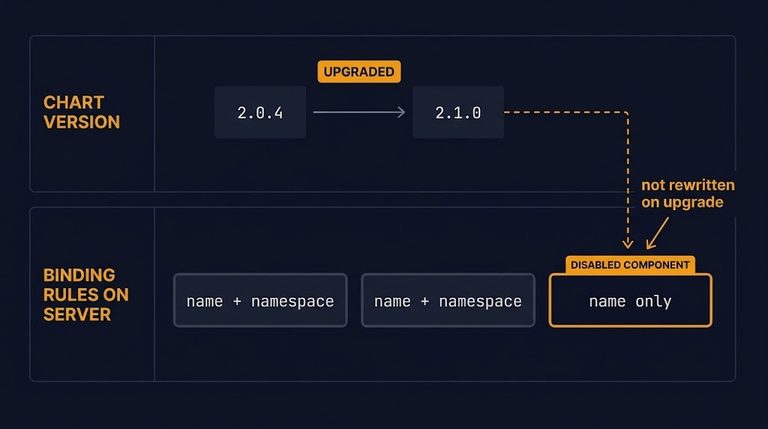
An upgrade to consul-k8s 1.8.18 or 2.1.0 does not rewrite binding rules for components disabled beforehand. A version inventory won’t show that. The rules on the Consul server will.
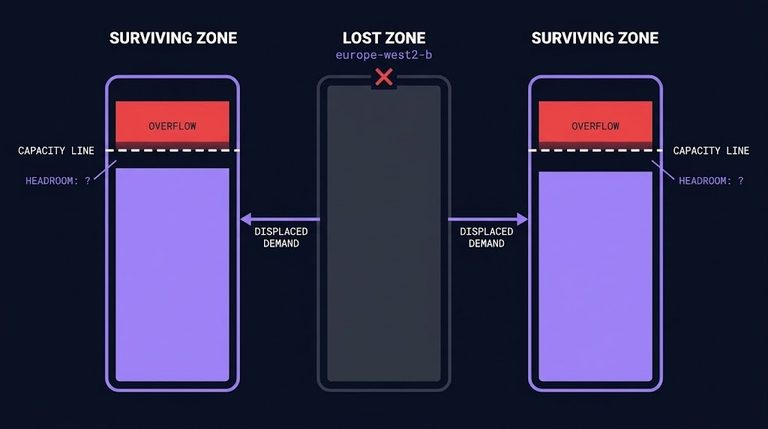
Google’s europe-west2 report describes a zone loss and then a second failure: surviving zones that could not absorb the displaced load. A zone-loss capacity test makes that second failure measurable.
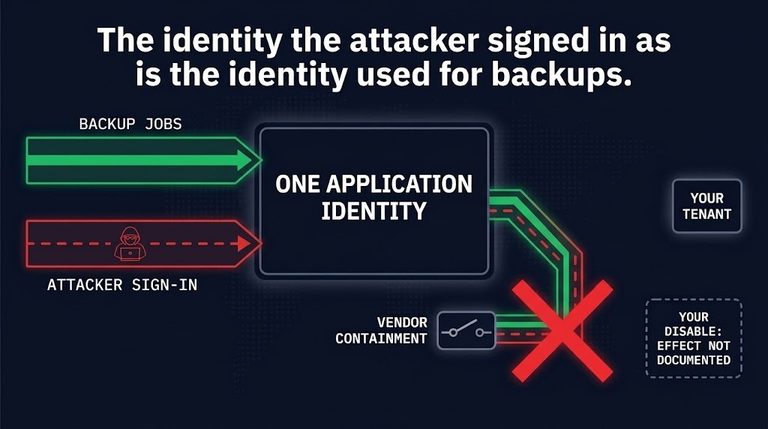
Backup application identity: the vendor’s containment suspended the service that ran on it. What the vendor controls, what a tenant administrator controls, and the restore-path check to record before the next incident.
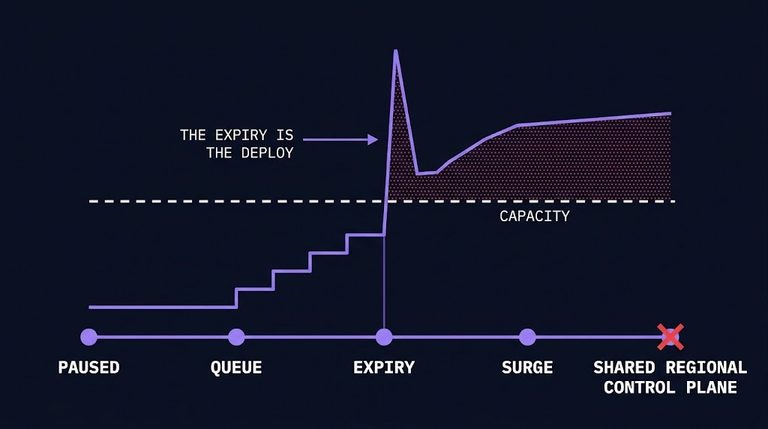
Azure’s post incident review for 7Q30-010 traces a gateway outage to a paused rollout that resumed all at once. Here is what it establishes, and two tests for your own holds and restarts.
CMS Category: Cloud Strategy (cloud-strategy). Prior Field Notes also carry field-notes, so please confirm at staging.
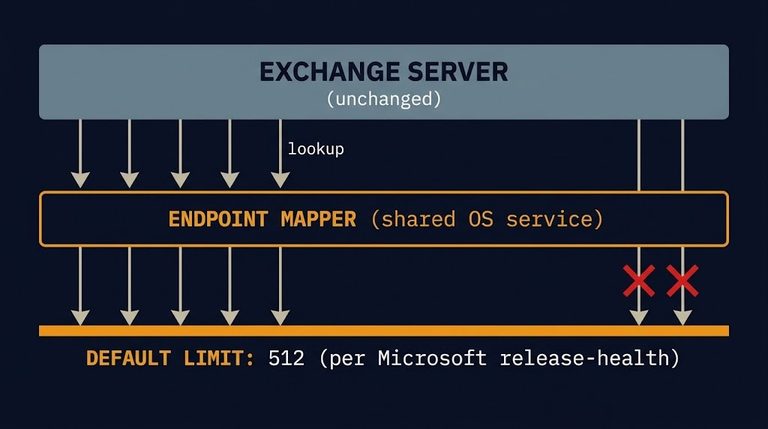
The Endpoint Mapper limit that Microsoft’s October 2026 Windows Server updates introduced is described in two Microsoft pages, and neither is the update notes that shipped with it. The October 13 cumulative updates for Windows Server 2025, 2022, 2019 and 2016 are documented in four notes. I read the improvement and summary sections of all…
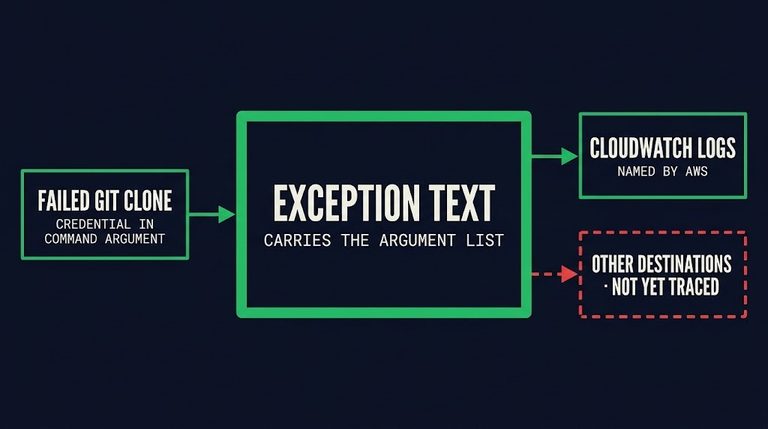
AWS bulletin 2026-134-AWS says a failed Git clone in the SageMaker Python SDK can write repository credentials to CloudWatch Logs. This note separates what AWS states from what the code shows, and derives rotation scope from where the output went.
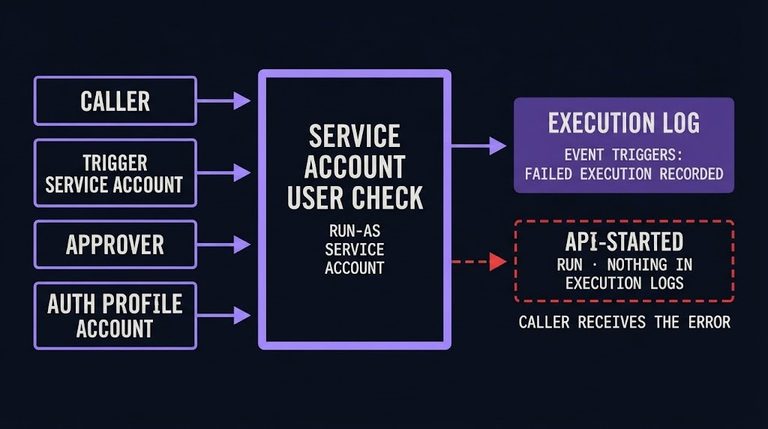
Google’s GCP-2026-068 bulletin adds a run-as service account permission check to Application Integration. The bulletin, the guide and the troubleshooting page describe different parts of it, and a denial does not show up in the same place twice.