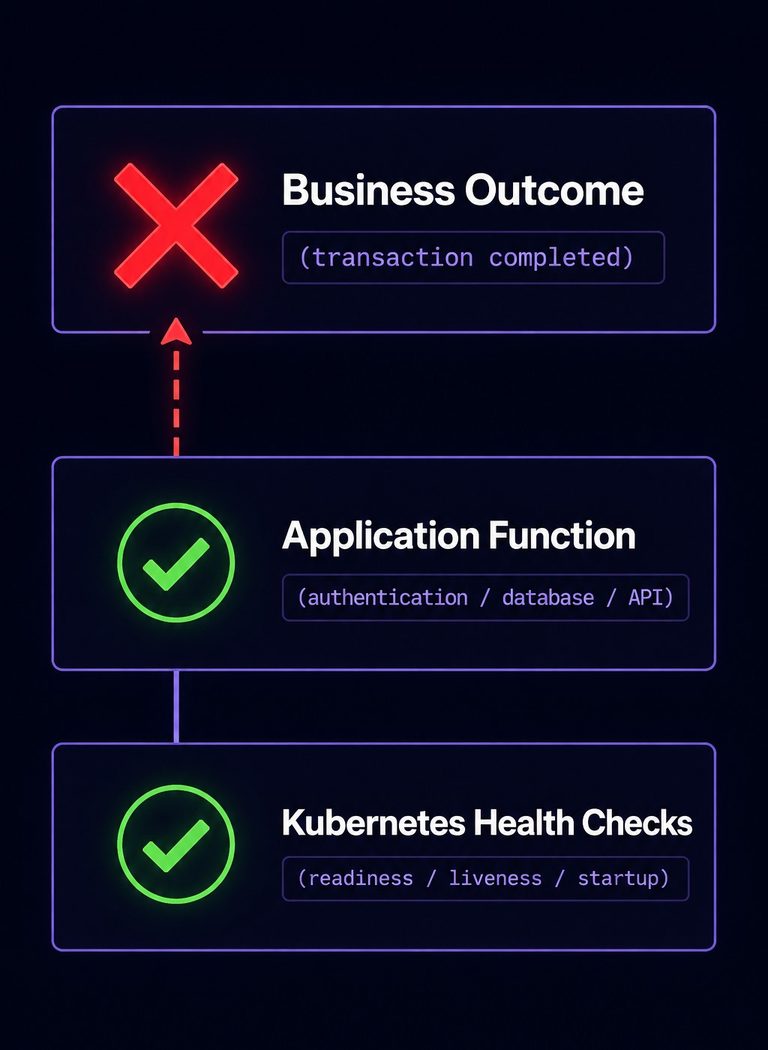
What Kubernetes Health Checks Actually Guarantee
Kubernetes health checks tell you whether a workload satisfies the narrow condition the probe was designed to test. They do not tell you whether…
READ MORE →ENGINEERING NOTES FROM THE COMPLEXITY GAP.
The journey from legacy infrastructure to modern cloud-native platforms is often obstructed by marketing-driven abstraction and tool-centric noise. Most technical journals focus on the "Day-1" installation — the easy path. Rack2Cloud documents the Day-2 production reality. We analyze how systems actually behave under load, at the boundaries of integration, and within the constraints of sovereign requirements.
Our field notes serve as a deterministic guide for the architect navigating the complexity gap. We prioritize the physics of data and the logic of high availability over vendor checklists.
"In production, complexity is the default state; architecture is the only defense."
Kubernetes health checks tell you whether a workload satisfies the narrow condition the probe was designed to test. They do not tell you whether…
READ MORE →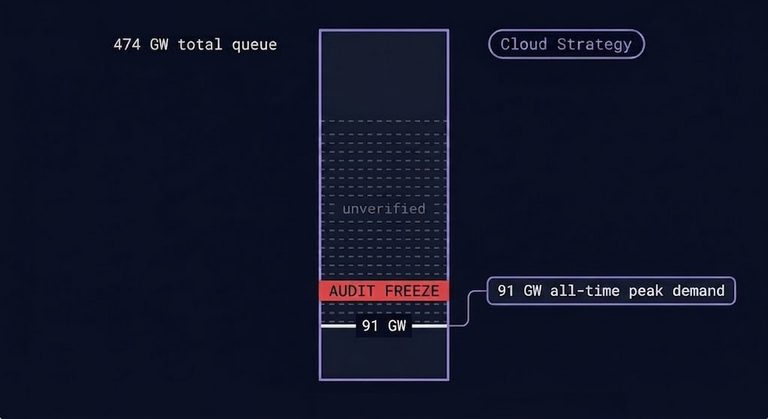
Phantom capacity is the planning problem underneath Texas’s decision to freeze new data center grid connections, and the problem has less to do with…
READ MORE →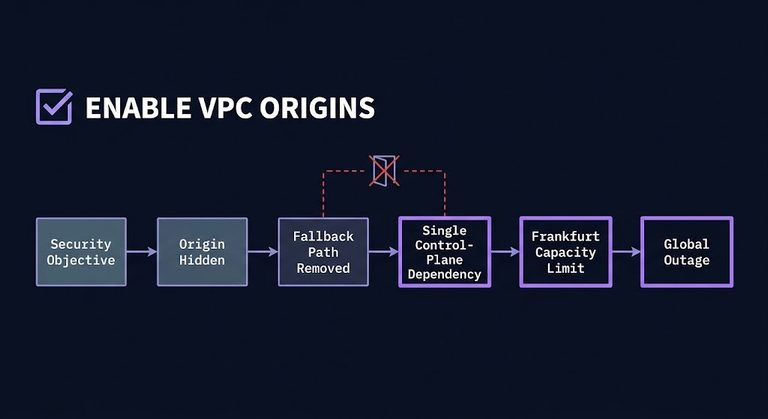
The AWS CloudFront outage on July 16 exposed a security reliability tradeoffs problem that most cloud architecture teams have never priced: the feature you…
READ MORE →
A session control gap — not a broken identity control — is why approximately 5.67 million Qantas customer records were compromised. No password was…
READ MORE →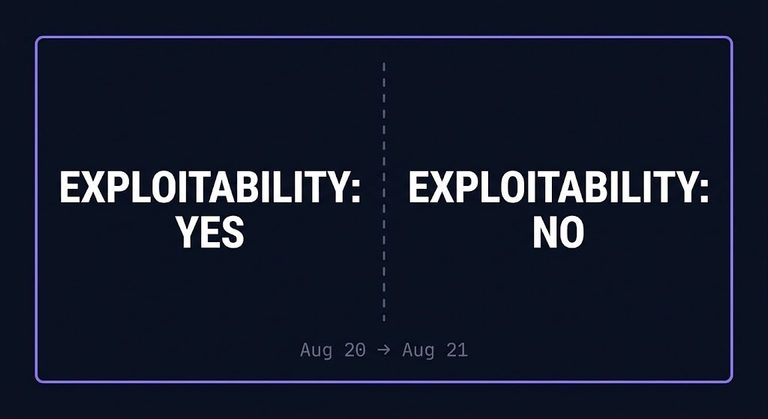
Verification asymmetry is what happens when the only party who can confirm whether your organization was compromised is the same party whose public account…
READ MORE →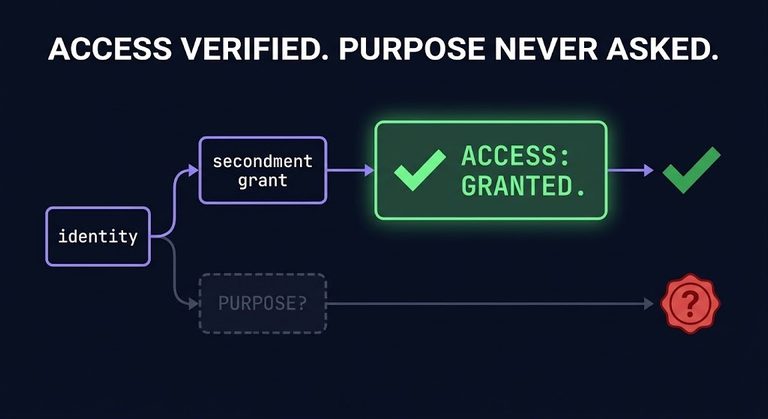
An access authorization gap — not a stolen credential, not a bypassed firewall — is what let two seconded employees look up the Australian…
READ MORE →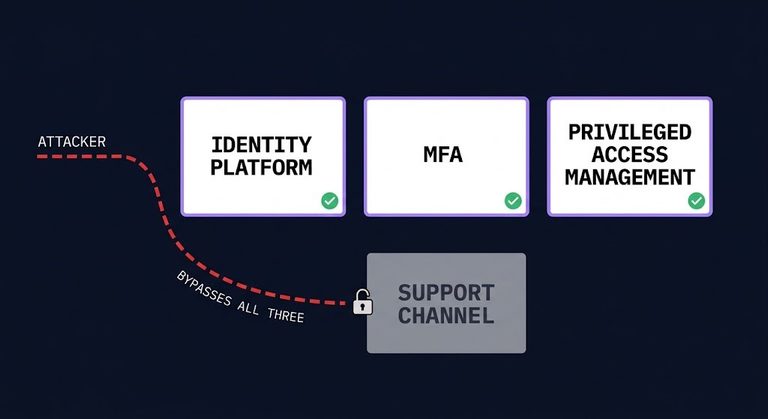
Help desk social engineering doesn’t defeat the identity platform, MFA, or privileged access controls — it bypasses the moment those systems were supposed to…
READ MORE →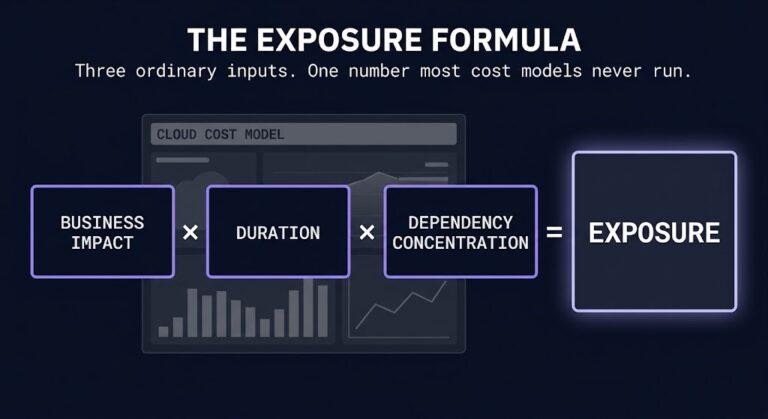
Cloud concentration risk has always existed — what’s new is that it’s starting to show up denominated in currency instead of uptime percentages. A…
READ MORE →
Identity directory egress is the blind spot sitting inside almost every enterprise security program: the moment a valid session reads more than it should,…
READ MORE →
AI consumption pricing broke the model executives used to govern infrastructure spend. One-third of business leaders — 33%, according to KPMG’s Q2 2026 Global…
READ MORE →
Most breach post-mortems that touch third-party cloud access get one detail backwards: they go looking for what broke, and in the Accenture case, nothing…
READ MORE →
Cloud governance failure domains emerge when governance becomes operational infrastructure instead of administrative oversight. Twenty years ago governance approved infrastructure. Today governance is infrastructure…
READ MORE →